OSCP · CRTO · CPTS - certified penetration testers
Findings from day one.Not week six.
Whether an auditor is asking, a customer is asking, or you would rather find it before someone else does - tested manually, not by scanner. Then watched between engagements, not filed away.
One year of cover
Watching365days a year
Covered three ways - not only on the days a tester is booked.
- 1
Tested manually
A pentester works the agreed scope and reports findings. Each finding appears in our PTaaS platform as discovered, with critical and high-risk email alerts, enabling developers to fix issues immediately.
- 2
Monitored daily
The same scope, re-checked every day in between, with a full scan weekly.
- 3
Scan on demand
Run one from your dashboard the day you ship a change - no booking, no waiting on us.
Monitoring and your own scans come with a continuing programme. A single assessment is the test and the hand-verified retest.
Day one
First finding, the day it is confirmed
5 to 10 days
Kickoff to testing complete, on a fixed price
Retest included
We verify your fix manually, at no extra cost
1 working day
We reply with scoping questions
10+
CVEs published
2000+
Vulnerabilities reported
20+
Clients served
50+
Engagements delivered
What you get
Three things, and the third is usually sold separately.
We think the test is not finished until somebody has checked that the fix worked - so checking is part of the price, not an extra.
A report built for whoever is asking
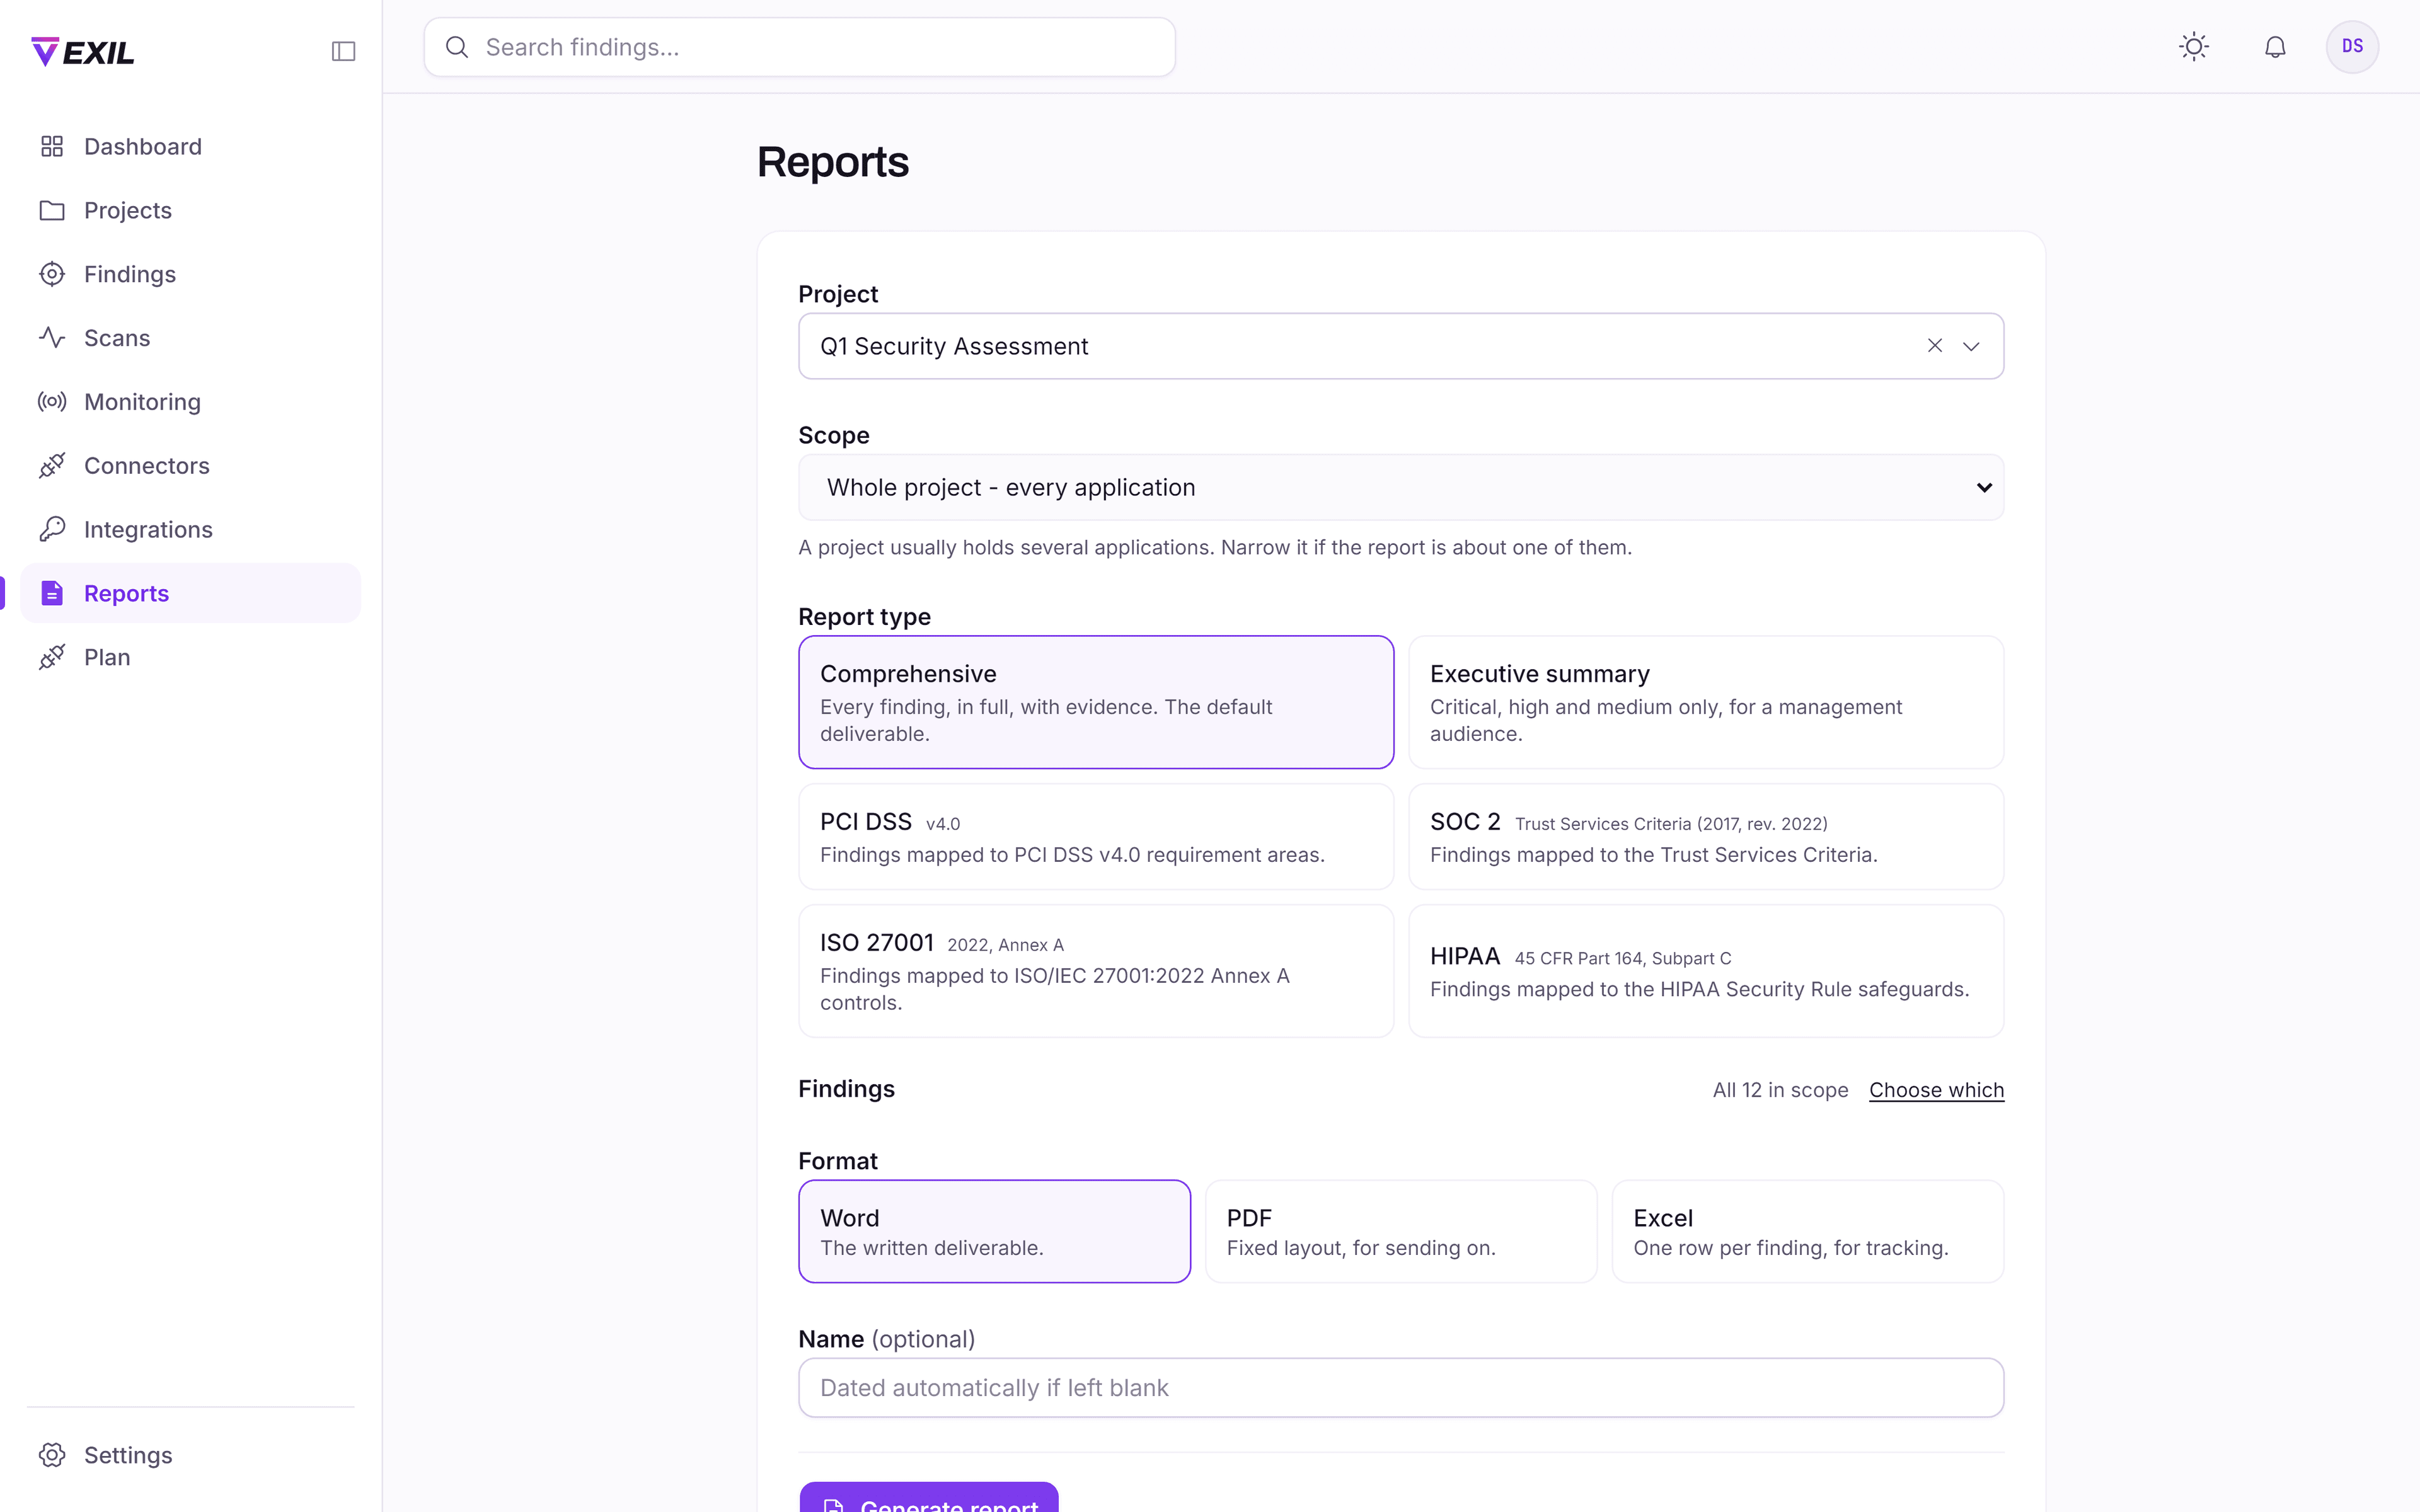
The same engagement, exported for your customer, your auditor or your board. Word, PDF or Excel - mapped to the standard that is asking.
Findings while we test
Each one reaches you the day it is confirmed, with the proof attached. Your engineers start on the worst of it in week one.
A retest that proves the fix
You mark it fixed, a tester checks it manually and records the verdict. Included in the price, not quoted as new work.
Who does the testing
People, and you will know which.
The people who test your systems have come from Big Four cyber practices, enterprise telecom and finance, and are credited with 10+ published CVEs.
Certifications say who is doing the work. What the work is run against - OWASP WSTG, ASVS, the API Top 10, PTES and OSSTMM - is set out with versions on how we test.
Testing
- OSCP
- CRTO
- CPTS
- CPENT
- LPT
- CRTP
- eCPPT
- eJPT
- CAPT
- CIPT
- ASCP
- TryHackMe PT1
Audit and governance
- ISO 27001 Lead Auditor
- ISO 27001 Lead Implementer
- CISA
These are certifications held by individuals, not company accreditations. We name the tester on your engagement before it starts, and you can talk to them during it.
The platform
This is what you get access to on day one
Not a login you receive with the invoice. Your workspace exists from the kickoff call, and fills up as the test runs.
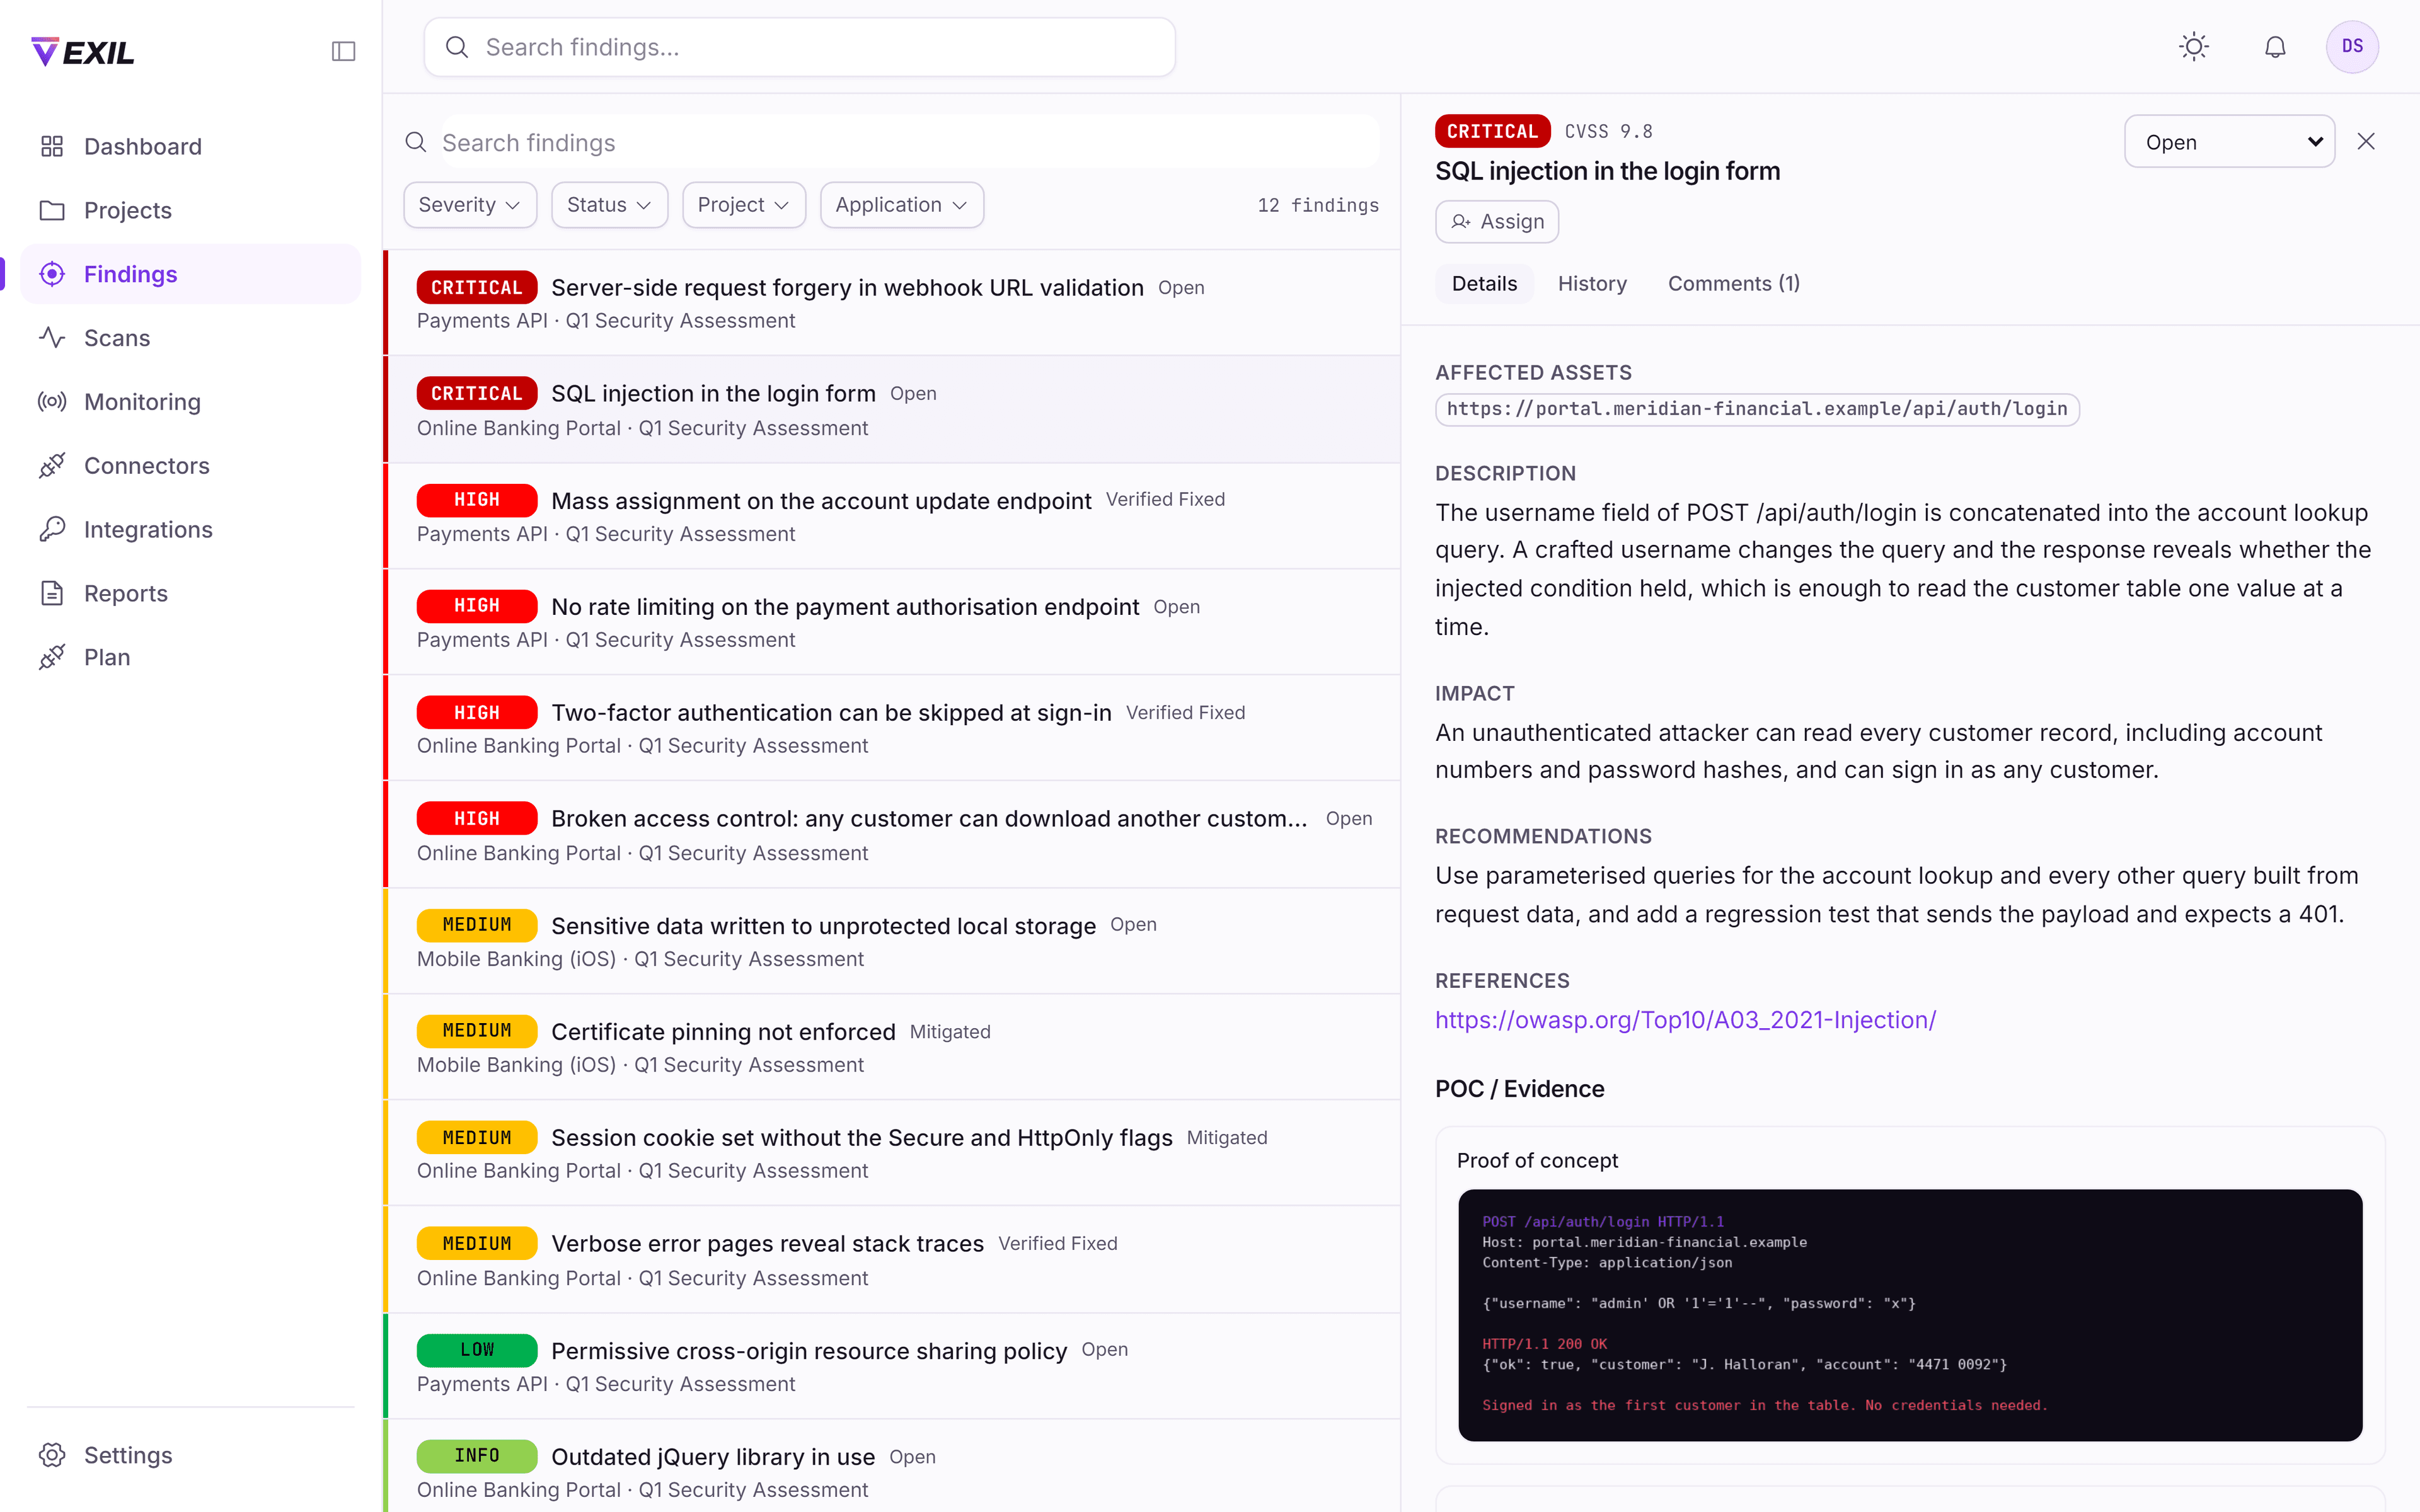
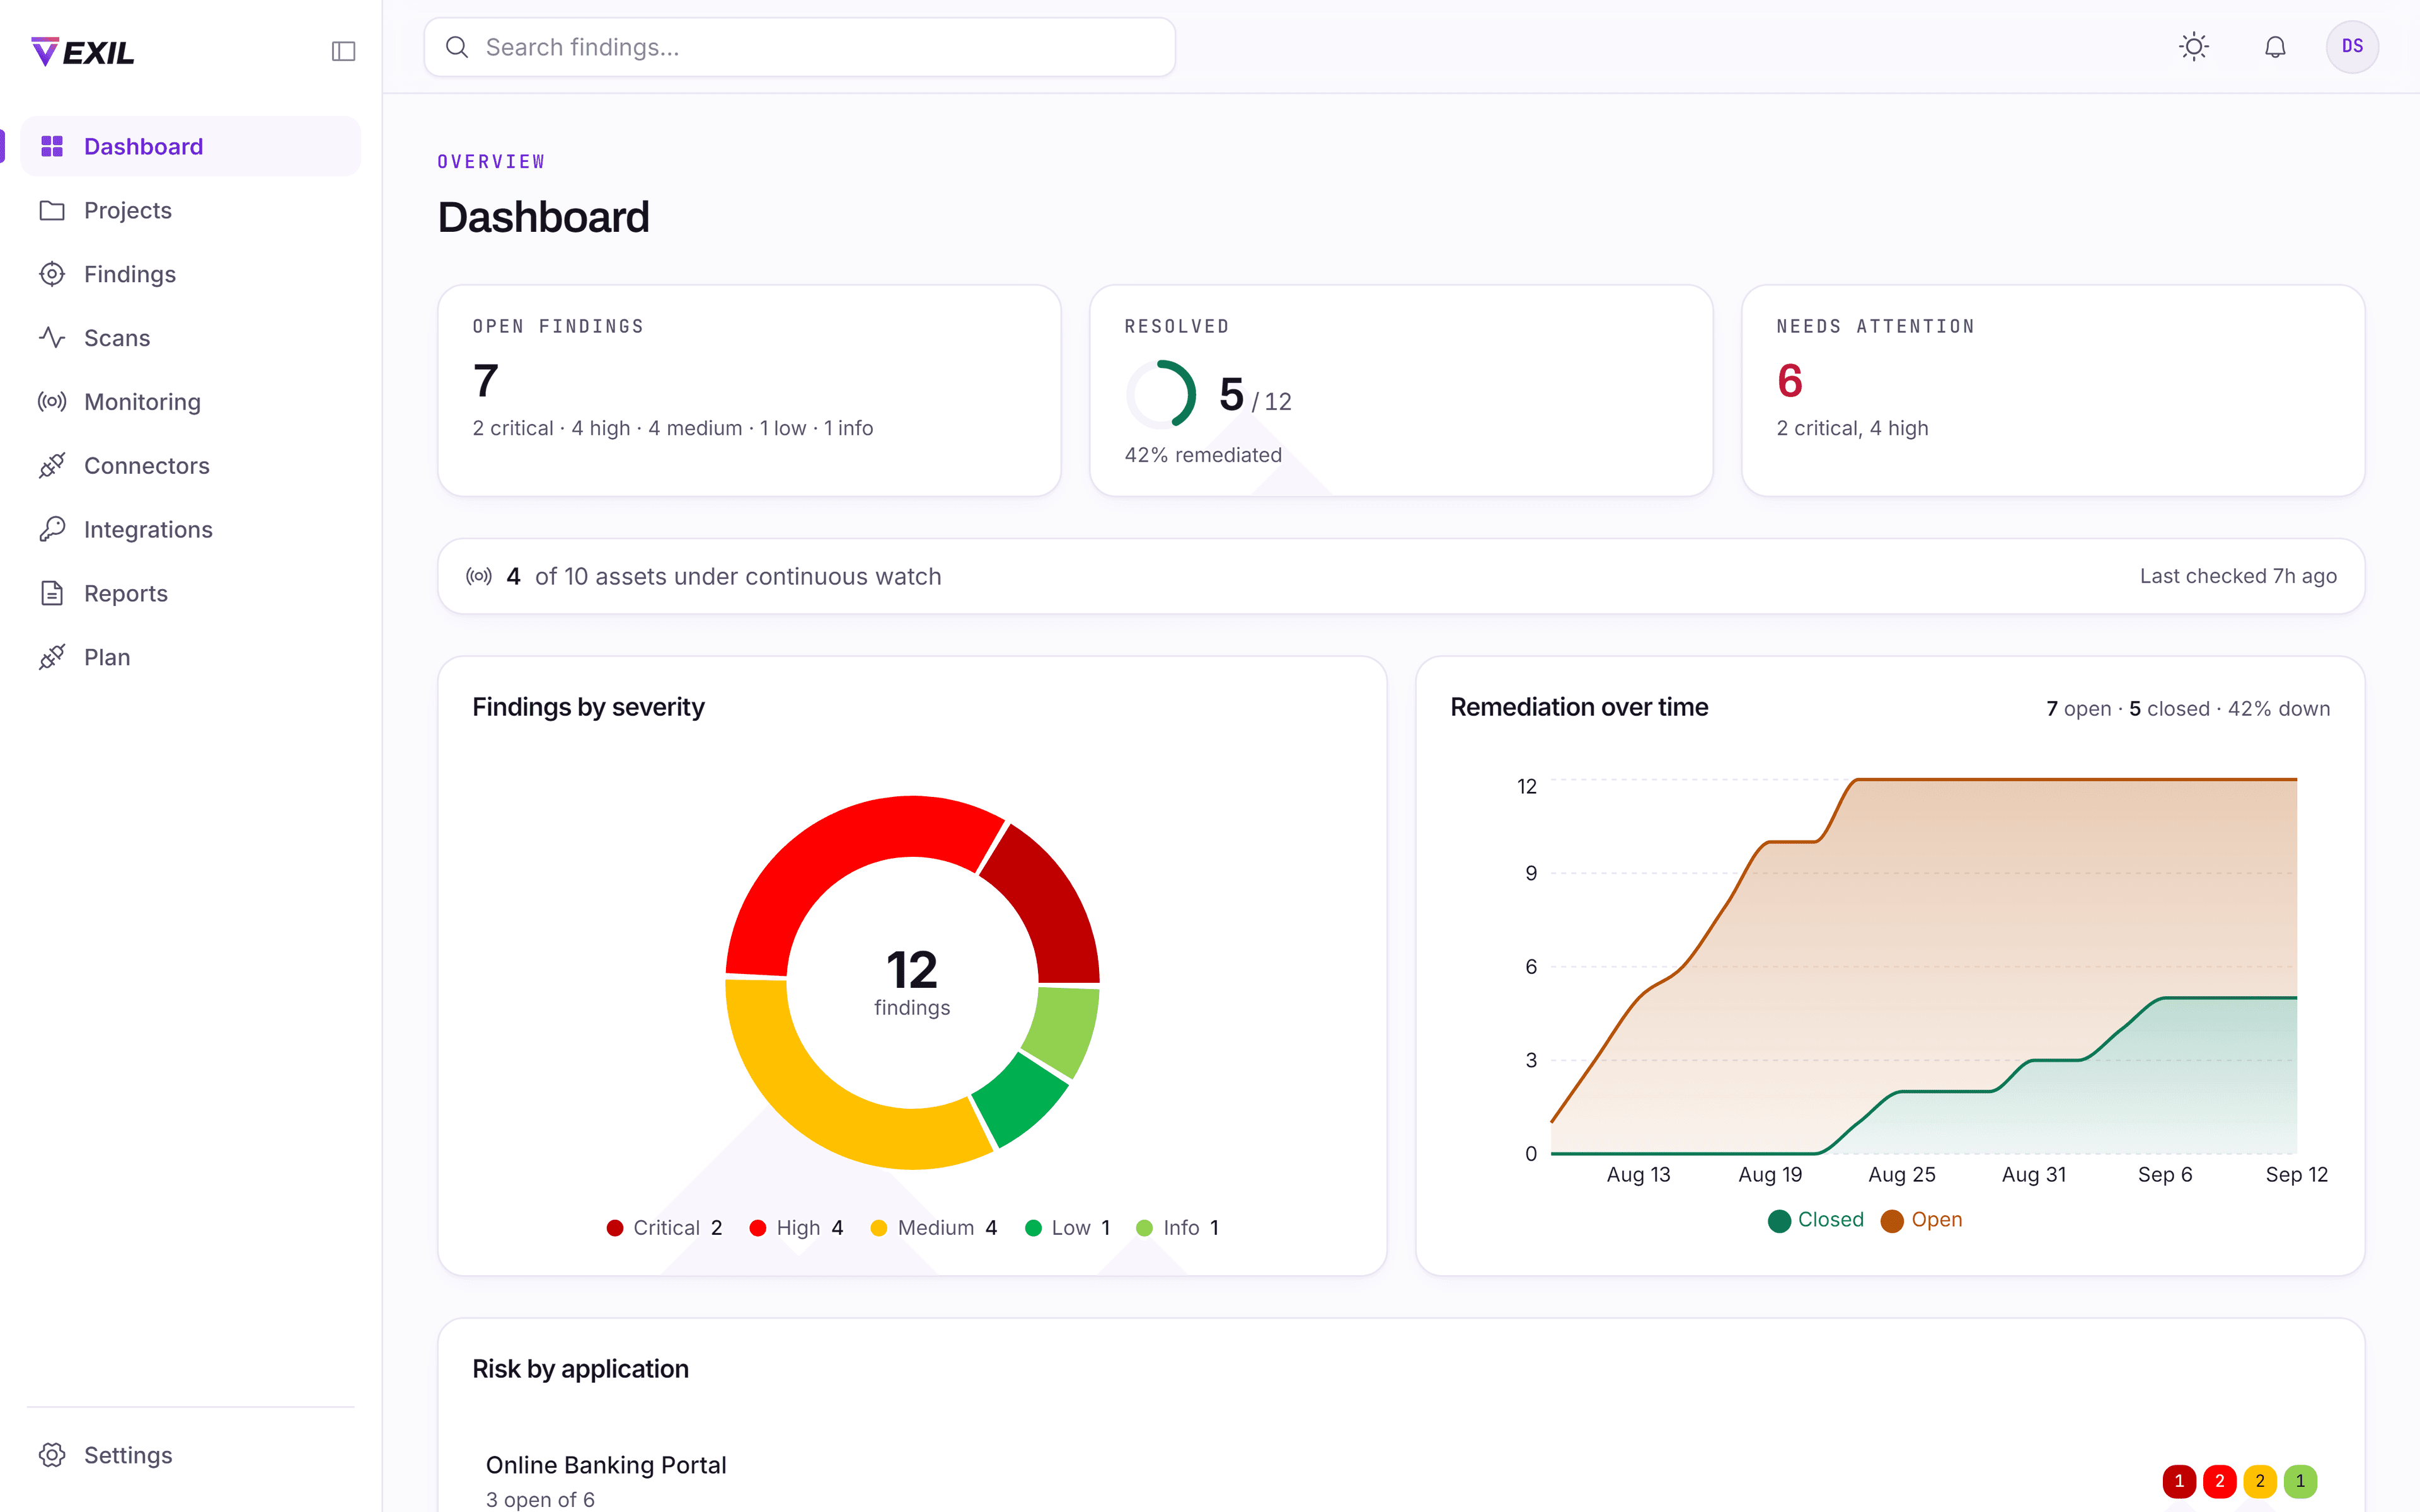
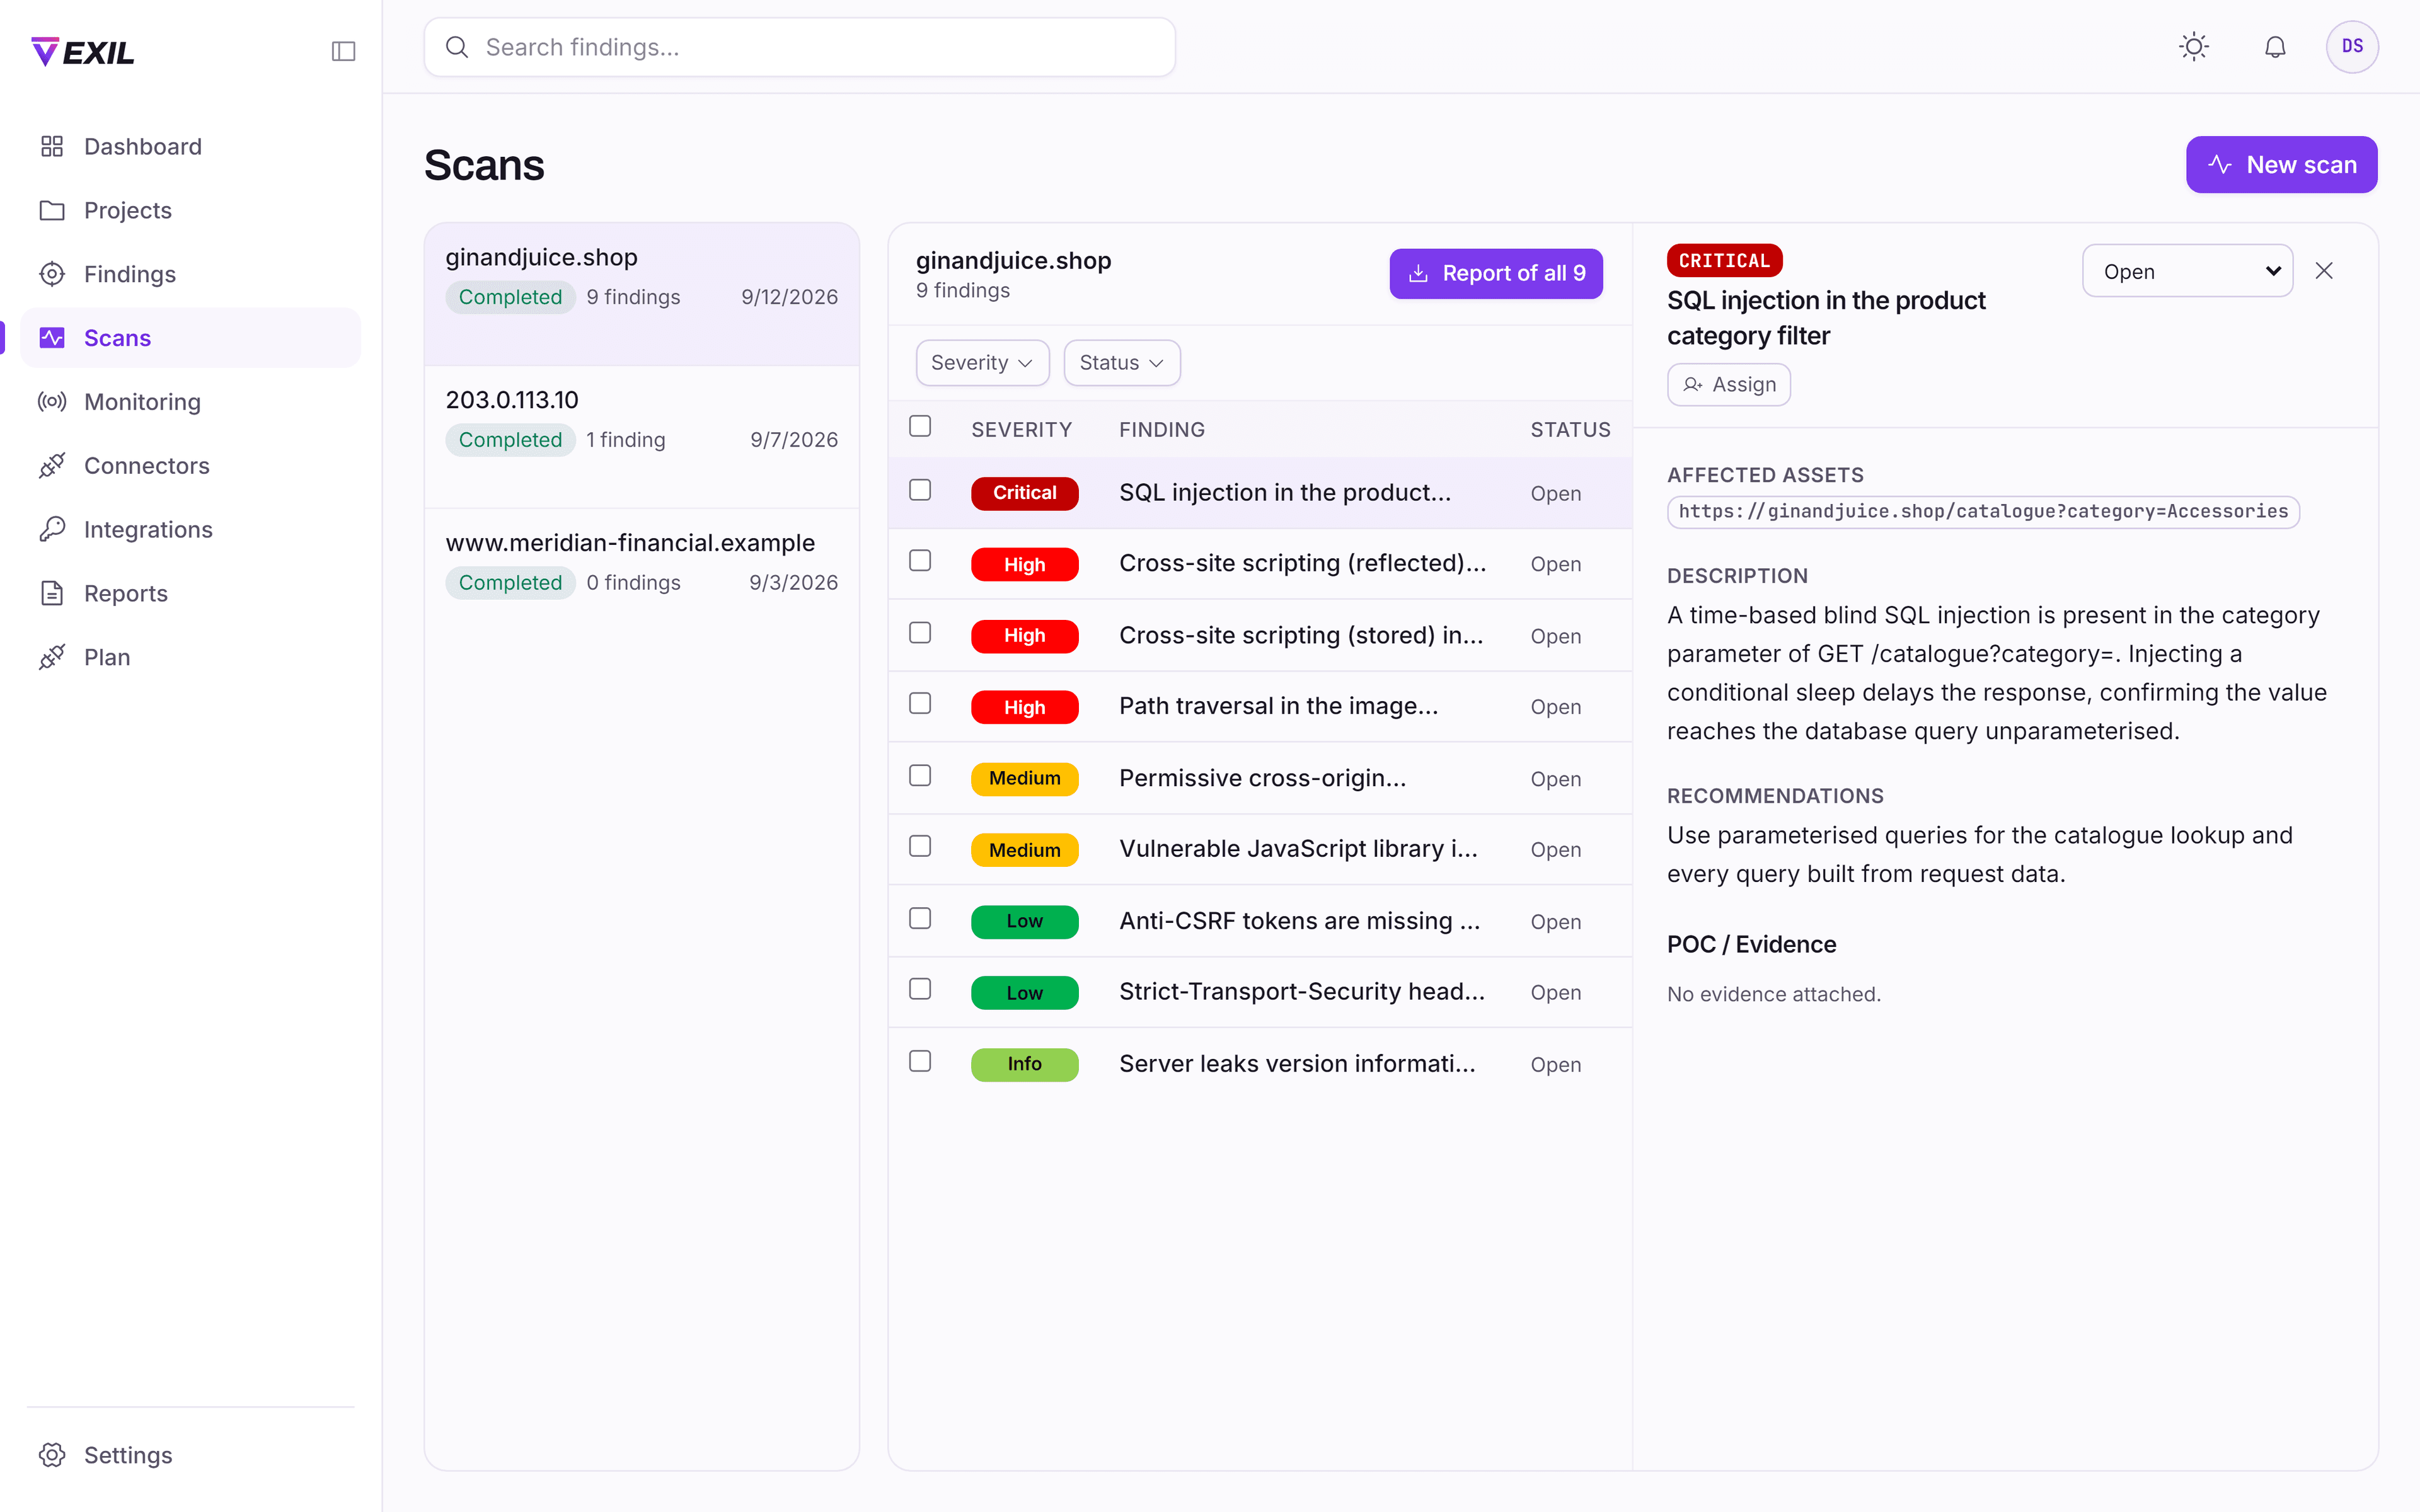
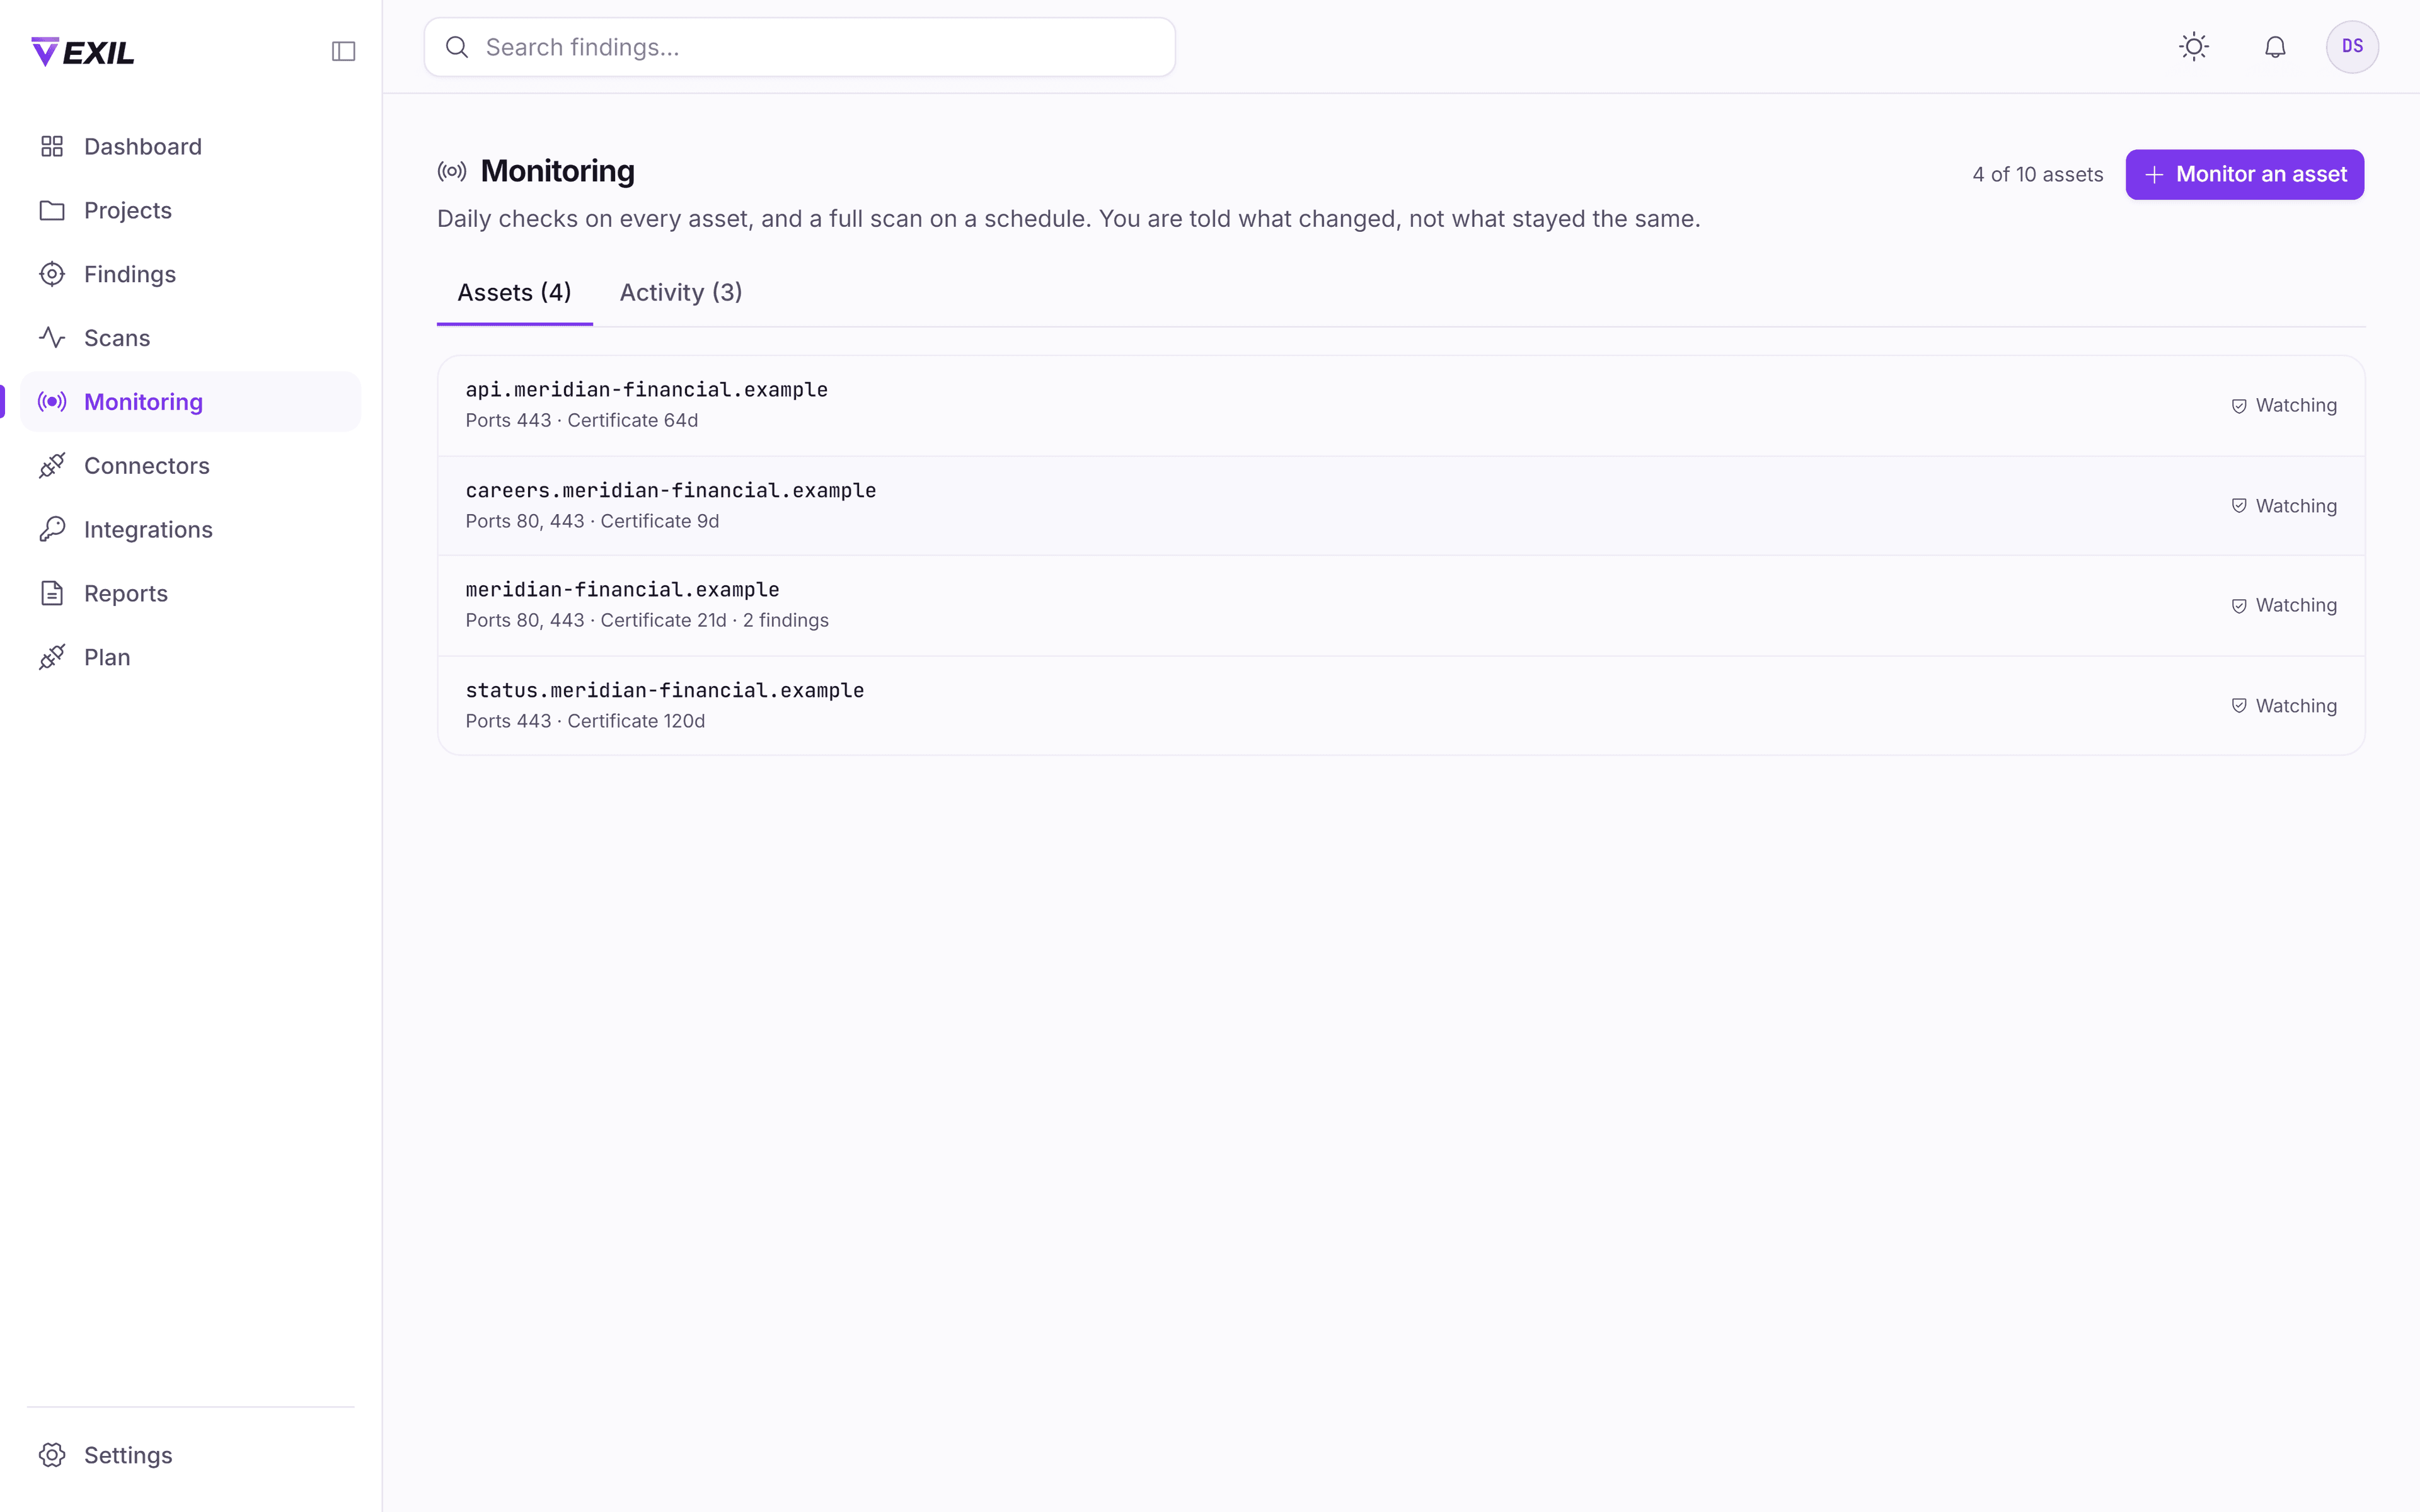
A finding, start to finish
You watch it move. Day one to a verified fix.
No waiting for a PDF at week six. A finding lands the day it is confirmed, and you follow it in your workspace until a tester has signed off the fix.
Vexil - one finding
Illustration- 1
Open - day one
Confirmed during the test and published to your workspace the day it is verified, with the request and response that prove it.
- 2
Assigned
Your engineer picks it up inside Vexil. The proof and the fix guidance travel with the finding; they see only the work that is theirs.
- 3
Fixed - retest requested
Your team marks it fixed and requests a retest from the same screen. One click, no new purchase order.
Retest passed
A tester checks the fix manually and records the verdict with the date and the tester. Included in the engagement, not billed as new work.
Every step is written to an append-only trail. Regenerate the report whenever you need it - Word, PDF or Excel, mapped to the framework that is asking.
An example finding, drawn in the platform’s own states. Demonstration data - a reserved .example host, no real client.
In their words
What clients said afterwards
Cybersecly conducted a thorough penetration test of our web application and APIs. Their team identified several critical security weaknesses that had been missed during previous assessments and provided clear remediation guidance. The final report was well-structured, actionable, and helped us improve our overall security posture significantly.
Head of Information Security, financial services We engaged Cybersecly to assess our SaaS platform before a major product launch. The consultants demonstrated strong technical expertise, excellent communication, and a practical approach to risk management. Their findings enabled our engineering team to address high-priority issues quickly and launch with greater confidence.
CTO, technology startup Cybersecly’s PTaaS platform transformed the way we handled penetration testing. Critical findings were reported immediately as they were identified, allowing our developers to begin remediation before the engagement was complete. The real-time dashboard, evidence tracking, and retesting workflow helped us resolve high-risk issues weeks faster than our previous assessment process.
Engineering Lead, SaaS Cybersecly truly IMPRESSED us with their work in VAPT & Review! Their attention to details and deep understanding made the project flow smoothly, and their professionalism exceeded our expectations. Working with such a team who’s quick to respond and consistently goes above and beyond was a genuine pleasure. 👏
CISO, AI company
Named and attributed on request, with the client’s permission. Most testing work is covered by an NDA, so we publish the role and the sector rather than the company.
Why a scan is not a test
“Can’t a scanner do this?”
For part of it. But the problems that cost you money sit behind a login, and a scanner cannot log in as two people and compare what they see. A person can.
Scanner
Finds what is there
- Open ports and services
- Publicly known vulnerabilities (CVEs)
- Default passwords
- Weak TLS, missing headers
- Outdated software
Fast, and worth running.
Tester
Finds what is broken
- One customer reading another’s data
- A regular user granting themselves admin
- A password reset that takes over an account
- A price changed in the browser and trusted
- Two safe steps chained into an attack
This is where the real risk is.
We run both, in that order. Tool output is kept separate from what a tester wrote, so you always know which is which.
Book a Free ConsultationCost
Fixed price, agreed up front.
We quote on scope, so there is no figure to put on this page. It is agreed before we start and it does not move.
What each engagement includesWhat decides it
Applications
How many
Size
Pages and endpoints
User roles
How many to test
APIs, networks
In scope or not
- What does it cost?
- It depends on what is being tested, so we quote rather than list. We will not give you a number and revise it later.
- When do I find out?
- On the scoping call, or straight after. Thirty minutes is usually enough, and the questions are published so there is nothing to prepare.
- What if the scope grows?
- We tell you what we found and what it would take to cover it. We do not invoice mid-engagement.
Four steps, and you can see all of them.
- 01
Scope
30-minute callWe map the attack surface, agree the rules of engagement and testing window, and give you a fixed price. Your workspace is created and your team is invited.
- 02
Test
5-10 working daysCertified testers work through the methodology manually. Findings appear in your workspace as they are confirmed, with evidence attached - you are not waiting for a report.
- 03
Remediate
Your timelineAssign findings to the engineers who own them. They see the work assigned to them, with the request, the response and the fix guidance in one place.
- 04
Retest
IncludedRequest a retest on anything you have fixed - the verdict lands in the same workspace. Then export the report your auditor, customer or board is asking for.
All four happen in Vexil, the workspace included with every engagement - which is why you can see step two while it is still running.
What we test.
- Offensive Testing
- VAPTWeb Application TestingAPI Penetration TestingMobile App TestingNetwork Penetration TestingCloud Configuration ReviewRed Teaming
- Assurance & Compliance
- Secure Code ReviewCompliance & ConsultingSOC 2 CompliancePhishing Simulation
- Monitoring
- Dark Web Monitoring
Scoped to what you actually have. All testing services
Tell us what needs testing.
A sentence is enough. We reply with the scope and what it would cost - no obligation, no sales sequence.